Closing the Software Supply Chain Risk
In today’s threat landscape, your software supply chain is one of your biggest blind spots. Every package, every dependency can become an open door for attackers. That’s why teams are embracing SBOM (Software Bill of Materials) as more than a compliance requirement.
An SBOM is the full inventory of your application. Every container image, every package, every transitive dependency—mapped and documented so you can see exactly what’s in your environment. The right SBOM doesn’t just tick a regulatory box—it accelerates triage, strengthens security posture and gives engineering teams answers in seconds:
- What’s in this container image?
- Which versions are running in production?
- Which packages have known vulnerabilities?
SBOMs Built Into the Pipeline
At JupiterOne, we designed SBOM capabilities with two priorities: real engineering needs and real risk reduction.
- Scan at the source — your registry
Point JupiterOne at connected GitHub or container registries. The collector scans images in place—no code shipping to third parties, no extra security risks. - Powered by trusted open source
Under the hood, we use Syft for SBOM generation and Grype for vulnerability detection—fast, accurate, and loved by developers. - Deep dependency visibility
We go beyond top-level packages. Every transitive dependency is mapped and linked, so if a vulnerability exists in a package, you’ll still see it—before attackers do. - Prioritization that reflects real-world threats
CVSS alone doesn’t tell you what’s dangerous right now. That’s why JupiterOne SBOMs integrate EPSS (Exploit Prediction Scoring System) so you can focus on the vulnerabilities most likely to be exploited in the wild.
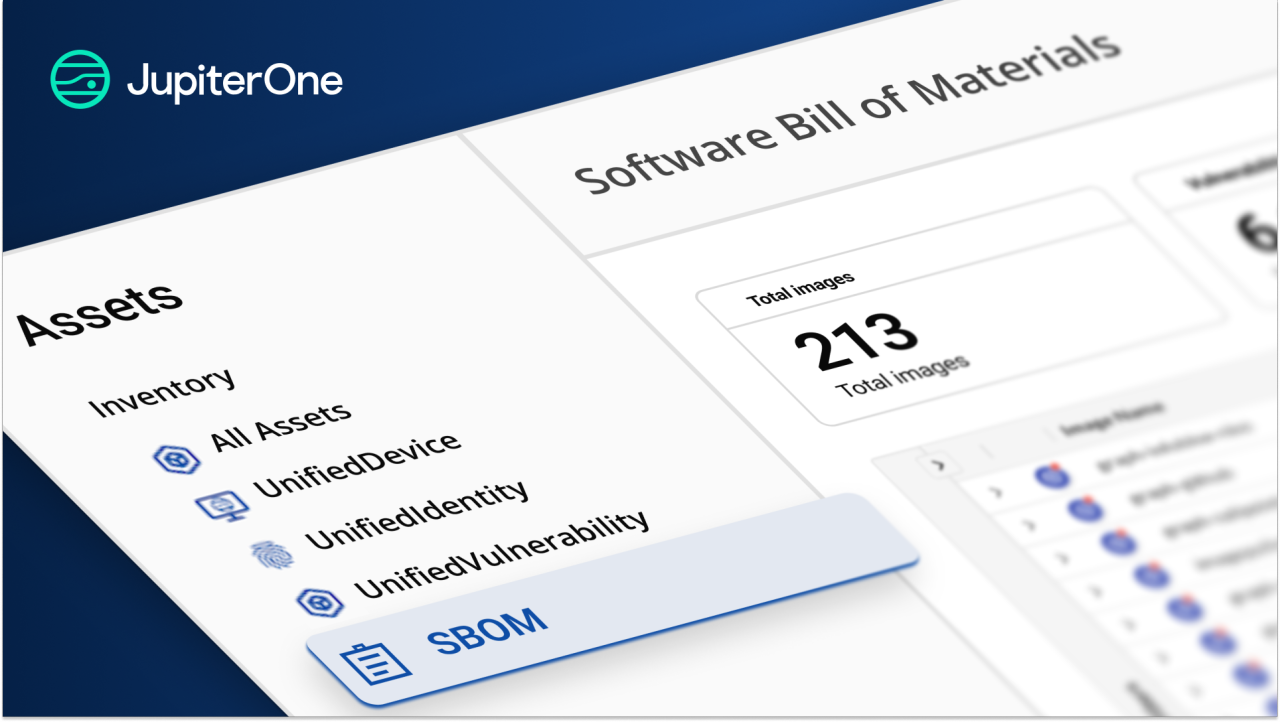
- Visualize and filter in the SBOM View
Access a dedicated SBOM View in JupiterOne to see high-level metrics, filterable tables of container images and code modules, and summaries of vulnerabilities—all in one place for faster investigation.

Case in Point: Log4Shell Without the Panic
When Log4Shell hit, most teams scrambled to identify where it lived in their environments—burning hours, even days. Today, JupiterOne customers can run a single query:
FIND CodeModule WITH name='log4j-core' AND version<='2.14.1'
RETURN connected Images, Owners, Environments
Within seconds, customers can see:
- Which images were affected
- Which environments they lived in
- Who owned them
And with EPSS data right there, they knew which ones to fix first.
Built for Scale, Reliability, and Velocity
If you’re running platform or security operations, you don’t just need SBOMs—you need them to keep up with modern delivery speed. JupiterOne delivers:
- Scale: Automatically scan every image in every registry—no manual babysitting.
- Reliability: Keep SBOMs current with every build. No stale data.
- Velocity: Give developers instant, searchable answers—without digging through repos or spreadsheets.
How to Get Started
- Start with production: Protect your most critical workloads first.
- Automate early: Make SBOM generation part of your CI/CD so it’s invisible to developers.
- Keep it queryable: Don’t bury SBOMs in a shared drive—make them live in JupiterOne where you can search, link, and act.
- Use EPSS for prioritization: Fix the vulnerabilities that truly matter first.