2019 Year in Review
Reflecting on the Past Year
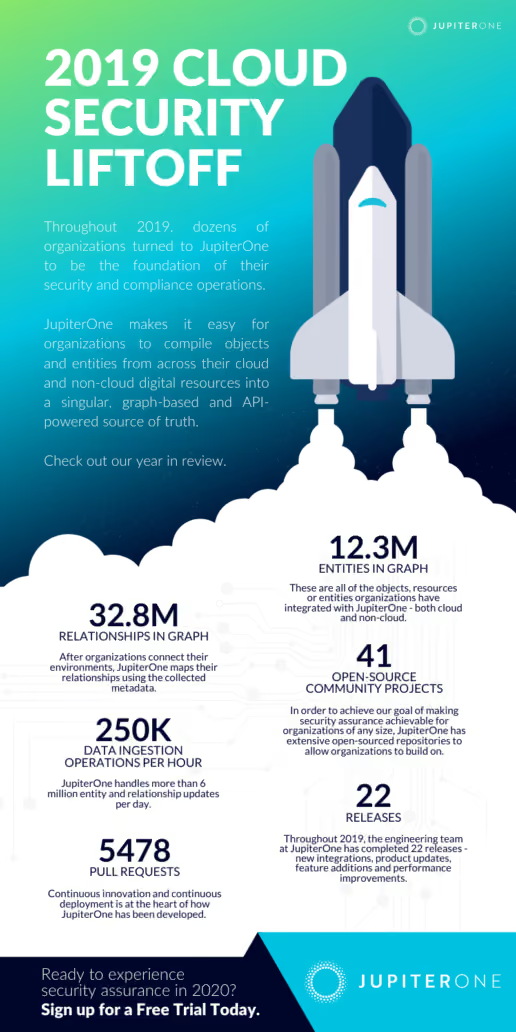
As we look forward to the last week of 2019, with 2020 patiently waiting for us, we wanted to dive into some of the data highlighting how JupiterOne is helping dozens of cloud-based organizations drastically simplify their security operations, streamline compliance management and proactively model threats.
Notable Integrations Highlights
Throughout 2019, the engineering team at JupiterOne completed dozens of new integrations with leading cloud providers and DevOps tools, including 30 AWS services alone! Here are just some of the notable integrations we added in 2019:
- Link Users with access to critical resources with your KnowBe4 security awareness trainings
- Connect Snyk security scans with code repos and the user that made the most recent changes
- Pull in more infrastructure resources with Azure and Openshift
- There is even more – Checkout the complete list
These integrations provide security teams with a context and depth of understanding they've never seen before. The centralization of management can reduce the time and effort it takes to complete routine security analysis as well as provides unparalleled visibility.
Threat Modeling, With A Query
There were a number of notable, public data breaches in 2019. Perhaps none more covered than CapitalOne. Normally, assessing similar risk when it comes to analyzing policies is almost impossible to complete in a timely manner. But, JupiterOne's querying provides tremendous flexibility, allowing security teams to perform 1 search and return actionable results in seconds. Yes. Seconds.
Green Pants - Seriously!
The JupiterOne team made their presence loudly known at the first Amazon re:Inforce conference. We proudly (and jokingly) list our green pants amongst our most treasured accomplishments for 2019. If you missed it, checkout our unofficial team photo.
Cheers to the New Year!
After an eventful 2019, we are excitingly looking towards 2020.
Happy Holidays and Happy Security – from the folks at JupiterOne.